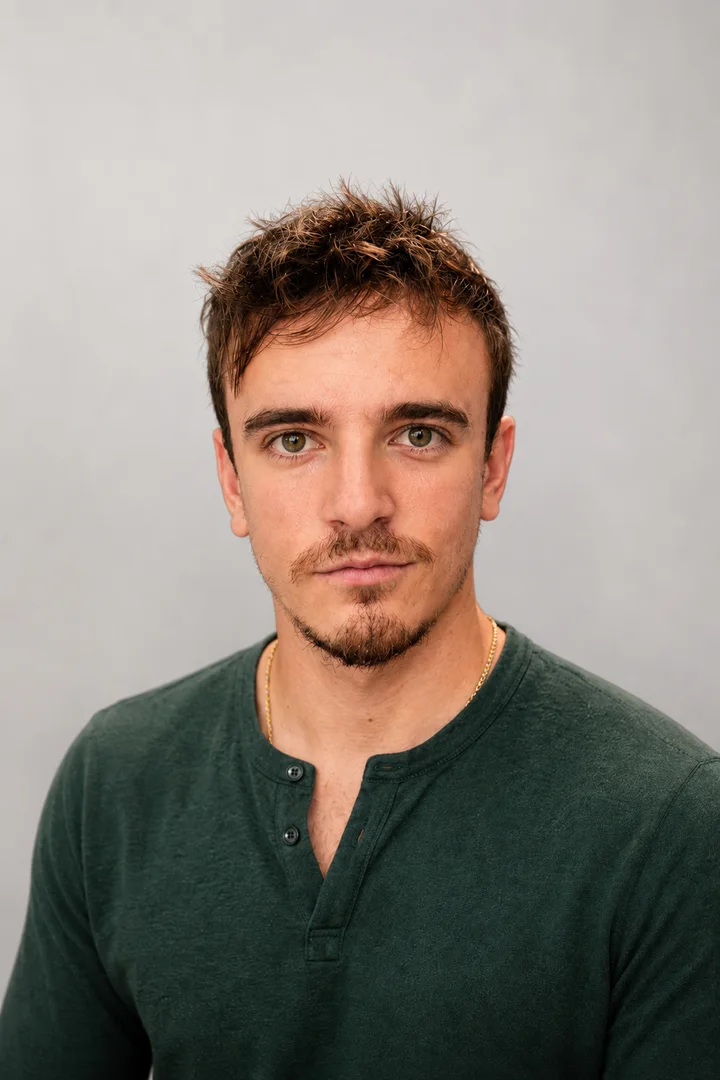
My path into cybersecurity
My curiosity about computer science began in middle school, when I taught myself to program. I went on to study Computer Science at the University of Turin, working alongside my studies to support myself. During university, I joined CyberChallenge.IT: that experience turned my curiosity about how systems work into a passion for cybersecurity. Today, I’m pursuing an MSc in Cybersecurity and continuing to learn through CTFs, security tooling, and running my own infrastructure.
I taught myself to program in middle school, then studied Computer Science while working to support myself. At university, CyberChallenge.IT sparked my passion for cybersecurity. I now pursue that interest through my MSc, CTFs, and security projects.
CyberChallenge & CTF practice
CyberChallenge.IT Finalist — 8th Edition, 2024
CyberChallenge.IT was the turning point in my path toward security. Attack/Defense practice connected my programming background with understanding vulnerable services and the traffic around them.
- Participated as a finalist in the 8th edition of CyberChallenge.IT in 2024, representing the University of Turin after training in web, binary, cryptography, network, and Attack/Defense challenges.
- Used Attack/Defense simulations to explore network traffic and attack patterns, turning a practical analysis problem into my BSc thesis project, CTF Hammer.
I continue practicing on Hack The Box machines and challenges, developing reconnaissance, exploitation, and documentation habits. Technical writeups help me make that learning explicit and repeatable.
Finalist, CyberChallenge.IT 2024 (8th edition), University of Turin. Attack/Defense simulations shaped my CTF Hammer thesis. Continued practice through Hack The Box machines, challenges, and technical writeups.
Selected security projects
CTF Hammer collects PCAP traffic from vulnerable hosts, parses conversations with tshark, classifies useful patterns, and streams results into a web interface. Async workers keep analysis away from the operator path; SSH/SCP and Docker Compose connect the pieces.
Tested during CyberChallenge simulations to review traffic and identify attack patterns in a unified interface.
Under heavy traffic, SSH/SCP connections degraded and risked saturating the vulbox network path. The prototype was therefore not used in the national final; throttling and resource controls informed the next iteration.
Tools: Flask · Svelte / SvelteKit · tshark · MongoDB · RabbitMQ / Celery · WebSockets · SSH / SCP · Docker Compose
Individual BSc thesis: a distributed Attack/Defense traffic-analysis tool using tshark, Flask, SvelteKit, MongoDB, RabbitMQ/Celery, and Docker Compose. Tested in CyberChallenge simulations; not used in the national final because traffic collection risked saturating the network.
A modular pipeline extracts features from HTA and JAR files, applies explainable heuristic rules, and can ask language models for a second assessment. CLI entry points and functional tests make each stage inspectable.
Tools: Python · BeautifulSoup · javap · Heuristics · LLM APIs · Tests
Python pipeline for static HTA/JAR analysis, explainable heuristics, optional model-assisted assessment, CLI entry points, and functional tests.
The team isolated services with Docker networks and modeled an attack chain from SQL injection to SSRF and an unauthorized Modbus write. It demonstrates applying security concepts to an OT/ICS-shaped environment—not professional industrial-security expertise.
Tools: Docker networks · SCADA simulation · SQL injection · SSRF · Modbus
Academic team project at Sabancı: simulated SCADA security with Docker network isolation and an SQLi → SSRF → Modbus attack chain.
Education & international experience
MSc Cybersecurity · Politecnico di Torino
Advanced study in cybersecurity with a direction toward infrastructure, container and network security.
Erasmus exchange · Sabancı University
One-year international study experience demonstrating independence, adaptability, English communication, and cross-cultural teamwork. Coursework included OT/ICS security and the AquaSecure collaborative project.
BSc Computer Science · University of Turin
Foundations in networks, operating systems, software development, and security. Thesis project: CTF Hammer.
Technical skills
- Infrastructure & container operations
- Linux-based Docker environments, service isolation, homelab operation, and controlled access.Linux · Docker · Docker Compose · Docker networks · Tailscale · Cloudflare Tunnel
- Security analysis & automation
- Python security tooling and application/network-traffic analysis demonstrated through CTF Hammer, malware analysis, and HTB.Python · tshark · Traffic analysis · Static analysis · Testing
- Web & distributed systems
- Connecting interfaces, APIs, workers, databases, and queues in end-to-end security projects.Flask · TypeScript / Svelte · MongoDB · RabbitMQ / Celery · WebSockets
Languages
Italian (Native) · English (C1) · French (Currently learning)
Additional work experience
Il MuMa · Front-of-House Manager
Coordinated front-of-house service, the team, and daily operations.
Osteria La Cantinella · Server / Front of house
Guest service and coordination with the front-of-house team.